Cybersecurity Analyst · Offense, Defense & Forensics
I don't call something fixed until I've tried to break it again.
CompTIA Security+ and CEH Master (practical and written)
MSc in Cybersecurity, in progress
Offense, network defense, and digital forensics
Looking for SOC Analyst roles
Four hands-on security engagements, each taken from initial compromise through to a verified fix or a defensible conclusion. I work the way an investigation actually goes: confirm the finding, prove impact, then write it up so someone else could reproduce every step.
Selected work
2026
Web application security
SQL injection to remote code execution, then closing every hole
Manual and automated SQL injection, an unrestricted file upload chained into RCE, reflected XSS, and an OSINT-built credential-stuffing attack, each scored with CVSS and paired with a verified fix.
Burp Suite · sqlmap · PHP/PDO · Apache hardening
Network security engineering
Five controls, one network, proven before and after
A zone-based firewall, a site-to-site IPSec VPN, a Suricata IDS with a custom signature, a Cowrie honeypot, and hardened Layer 2 switching, each with independent functional proof, not just a config dump.
Cisco IOS · Suricata · Cowrie · IPSec/IKEv1
SOC investigation
Tracing a cryptominer back to the exploit kit that dropped it
Full Security Onion investigation of a real malware capture, from a RIG Exploit Kit landing page through Smoke Loader to an active XMRig session, correlated across Sguil, Zeek, and raw packet analysis into IOCs and a framework-mapped remediation plan.
Security Onion · Wireshark · VirusTotal · MITRE ATT&CK
Digital forensics
Reconstructing an insider theft across disk, memory, and network
A premeditated data theft hidden inside a JPEG with end-of-file steganography, reconstructed by correlating Autopsy, Volatility 3, and Wireshark evidence, with a hash-verified chain of custody and a matrix that separates conclusive findings from single-source guesses.
Autopsy · Volatility 3 · Wireshark · MITRE ATT&CK
Writeups
September 2026
The search box that gave up the whole database
A single unescaped parameter in a travel booking app's search page turned into five separate findings: full database exposure, remote code execution, stored credential theft, and a working exploit chain between all three. Here's what actually changes once each one gets fixed.
September 2026
The best finding in my investigation was the one that turned out to be nothing
Investigating a staged insider data theft, I built a table rating every finding as conclusive or merely indicative, based on how many independent evidence sources actually backed it up. The single most useful row in that table is the one that says a suspicious lead was actually benign.
Certifications
In progress
MSc Cybersecurity
Postgraduate degree
2026
CEH Master
EC-Council, practical and written
2025
CompTIA Security+
CompTIA
About
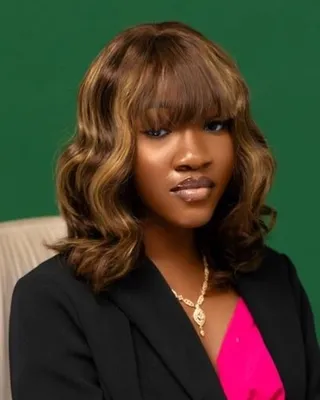
I came into cybersecurity through hands-on lab work rather than a single incident that convinced me: penetration testing, building and hardening a network from scratch, and reconstructing what happened after something already went wrong. Each of those is a different discipline, and I wanted to be genuinely competent at more than one before deciding which to specialise in.
What carried across all three: the finding only matters if you can prove it. In the forensics work that meant rating evidence as conclusive only when two independent sources agreed, and saying so plainly when something looked suspicious but turned out to be benign. In the pentest it meant not just exploiting a vulnerability but writing the fix and confirming it couldn't be bypassed. That habit is what I want to bring into a SOC seat.
Ruling something out is still a finding. I write those down too.
Contact
Currently completing an MSc in Cybersecurity and looking for a SOC Analyst role.